Categories
Uncategorized

Ten Years, Three Plans – How ASIC’s Corporate Plan Has Changed, and What It Tells Us

Every August, the Australian Securities and Investments Commission publishes a corporate plan. On the surface it is a compliance document, required under the Public Governance, Performance and Accountability Act 2013. In practice it is one of the clearest signals a regulated business gets about where the regulator’s attention, and its enforcement resources, are heading over the next four years.
With ASIC’s latest plan hot off the press this month, we thought it was the perfect opportunity to step back and take the long view: to line the newest edition up against those that came before it and see just how much the regulator’s priorities, language and posture have shifted over a decade.
So we pulled three of them off the shelf (2016, 2021 and 2026) and read them side by side. Ten years apart at the bookends, five years between each. What emerges is a changing idea of what ASIC is for, written each time in the language of whichever crisis or inquiry had most recently reshaped the environment. Each plan is very much a product of its moment.

The three moments
It helps to remember what each plan was written into.
The 2016 plan (covering 2016–17 to 2019–20) was Greg Medcraft’s, and it landed less than a decade after the 2008 global financial crisis. The GFC is never far from the surface. The plan opens on the language of trust, confidence and “gatekeepers,” and it reads as a document still processing the lesson that markets can break and that the public’s faith in the financial system is fragile and hard-won.
The 2021 plan (2021–22 to 2024–25) was Joseph Longo’s first as Chair, written roughly eighteen months into COVID-19 and, more importantly for its character, two years after the Hayne Banking Royal Commission handed down its final report in February 2019. The Commission’s findings run right through the document: in its emphasis on misconduct, on the Financial Accountability Regime, on design and distribution obligations, and on ASIC’s re-cast identity as “a strong and targeted law enforcement agency” and “an active litigator.”
The 2026 plan (2026–27 to 2029–30) is Sarah Court’s first, and it reflects a regulator operating in a genuinely new risk landscape (artificial intelligence, cyber and operational resilience, private markets and private credit, digital assets) and one that, after years of rebuilding its enforcement capability, is visibly more confident. Court came to the chair as ASIC’s deputy and a career litigator, having overseen what the government described as some of the agency’s strongest enforcement results on record. That self-assurance shows.

The language: from “trust and confidence” to “harder to avoid”
The most striking shift over ten years is tone.
The 2016 plan is earnest and almost academic. Its central vocabulary is trust, confidence, culture, gatekeepers and behaviour. Medcraft’s message dwells on “human behaviour drivers” such as financial literacy, behavioural biases, incentives and deterrence, and frames ASIC’s role as understanding why people and firms act as they do. There is a diagnostic, social-science quality to it. The recurring promise is to “detect, understand and respond.”
By 2021, the register has hardened. Longo’s message is built around the language of misconduct, disruption, deterrence and enforcement. ASIC “will remain an active litigator against misconduct” and will “use our full suite of tools and powers to address wrongdoing.” Where 2016 wanted to understand behaviour, 2021 wants to identify, disrupt and deter it. This is the vocabulary of a post-Royal-Commission regulator that had been publicly criticised for being too soft.
By 2026, the language shifts again, this time toward balance and confidence. Court’s framing is that ASIC will be “easier to deal with for those trying to comply with the law, while being harder to avoid for those causing harm.” The plan repeatedly insists it does not have to “choose between strong regulation and growth”; it can and must have both. Words like productivity, growth, innovation and resilience now sit alongside enforcement. This is the language of a regulator that no longer feels it has to prove it can bite, and can therefore afford to talk about being a partner to well-behaved business.

Areas of focus: what each plan actually points at
The headline priorities tell their own story.
2016 organised itself around five “long-term challenges”: aligning conduct with trust and confidence; digital disruption and cyber resilience; structural change (led by the growth of superannuation); complexity driven by financial innovation; and globalisation. Notably, cyber is present but framed abstractly, as “digital disruption and cyber resilience,” an emerging theme rather than a live threat.
2021 reorganised around a cleaner set of external strategic priorities: promoting economic recovery (a COVID artefact); reducing consumer harm from poor product governance and scams “in a low-yield environment”; enhancing cyber resilience; and driving industry readiness for the wave of law reform flowing from the Royal Commission, including the Financial Accountability Regime, breach reporting, and design and distribution obligations. The through-line is implementing the Commission’s agenda.
2026 presents five strategic priorities: improving consumer and small business outcomes; strengthening professional conduct and access to reliable information; supporting better retirement and superannuation outcomes; supporting effective, resilient and innovative operations; and driving integrity, transparency and confidence across markets. Underneath sit focus areas that simply did not exist in comparable form a decade earlier: the impact of AI use, digital asset platforms, private credit practices including valuations and liquidity, mandatory climate reporting, and scam prevention and disruption as a first-order concern rather than a footnote.
Two structural moves are worth flagging. The first is that private markets and private credit have arrived as a headline preoccupation. The 2026 plan explicitly targets “changing risks, interconnectedness and supervision across private markets” and the distribution of private credit funds to retail clients. This reflects the migration of risk out of the well-lit public markets and into less transparent alternative investments, and it is arguably the single biggest new area of focus. The second is that AI appears on both sides of the ledger: as a risk ASIC must police (AI-driven market manipulation, deepfakes, unreliable financial information) and as a capability ASIC intends to use itself to regulate more effectively.

The risks identified
Read the risk framing closely and you can date each plan almost to the year.
In 2016 the shadow is the GFC. The plan states plainly that ASIC’s system “is not designed to eliminate market risk, prevent all wrongdoing, or ensure compensation for all investors who lose money,” a sober, almost defensive acknowledgement of the limits of regulation that reads as a direct lesson of 2008. Its economic environment section frets about household debt at record highs (186.9% of disposable income), property oversupply, soft commodity prices and global volatility. The animating concern is systemic fragility and the risk of another confidence-destroying shock.
In 2021 the shadow is the Royal Commission. The identified risks are overwhelmingly about conduct and consumer harm: poor product governance and design, scams, and the risk that firms fail to lift their standards to meet incoming reforms. The plan commits explicitly to working with government “to implement the law reforms responding to the Royal Commission.” Cyber has by now graduated to a standalone strategic priority. The animating concern is that the misconduct the Commission exposed might be allowed to persist.
In 2026 the concern is complexity, technology and interconnection. Its operating-environment analysis is the most sophisticated of the three. It warns that “operational risks are becoming increasingly system wide,” that reliance on shared service providers and platforms allows “disruptions to transmit rapidly across entities and sectors,” and that “uncertainty has become a structural feature” of a fragmented geopolitical and economic order. It names AI as transforming the environment, superannuation assets exceeding $4.5 trillion and consolidating into a handful of giant funds, climate-driven extreme weather pressuring insurance, and private credit as an opaque and growing risk. The animating concern is speed and contagion: in a digitised, interconnected system, harm now spreads faster than the regulator can see it.

How the plan is approached: from framework to focus
The three documents also differ in how they are built.
The 2016 plan is the most conceptual. It is heavy on the strategic architecture, the “detect, understand and respond” model, the “what good looks like” narrative for each sector, and the behavioural theory that underpins it all. It reads as a regulator explaining its philosophy.
The 2021 plan is more of a delivery plan. It splits neatly into external and internal priorities, ties itself tightly to the government’s Statement of Expectations and ASIC’s Statement of Intent, and organises its actions around discrete reform programs. It reads as a regulator executing an agenda largely set for it by others, namely the Commission and the Parliament.
The 2026 plan is the most operational and granular of the three. Under each of five priorities sit specific, named surveillance and enforcement activities: reviews of debt collectors, “disaster chasers,” buy-now-pay-later providers, separately managed accounts, private equity valuation practices, and wholesale broker preparedness for market shocks. It reads less like a philosophy and more like a work program from a regulator that knows exactly which doors it intends to knock on. There is also a new confidence in structure, including a “corporate plan on a page,” explicit budget forward estimates, and a clearer separation of the Chair’s executive authority from the Commission’s strategic role.

The signal from the Chair
If you read only the Chair’s foreword, you would still catch the drift of each decade.
Greg Medcraft (2016) signals a regulator focused on capability-building and understanding. His message is preoccupied with data: a new chief data officer, a data governance council, a behavioural insights team, and the additional government funding that would let ASIC run “more proactive surveillances.” The tone is that of an institution investing in its own intelligence, still finding its feet as a law-enforcement body.
Joseph Longo (2021) signals resolve and rehabilitation. His message is unambiguous that ASIC “will continue to be a strong and targeted law enforcement agency” and “an active litigator.” It is the voice of a Chair repositioning a regulator that had been found wanting, determined to demonstrate teeth while managing a heavy reform-implementation load.
Sarah Court (2026) signals confidence and balance. Her message leads not with enforcement but with productivity, growth and responsible innovation, and with the observation that “how we regulate is as important as what we regulate.” The enforcement posture is now taken as read; it is the settled foundation from which she can talk about being easier to deal with for the compliant. Given her own background as a litigator who spent five years rebuilding ASIC’s enforcement capability, this is a Chair speaking from strength rather than reaching for it, a regulator emboldened by a run of success in the courts and comfortable enough to lead with the carrot because everyone now knows about the stick.
A few other comparisons worth noting
Superannuation has moved from the wings to centre stage. In 2016 it was cited mainly as a driver of “structural change.” By 2026 it commands an entire strategic priority of its own, with $4.5 trillion in assets, an ageing population and 2.5 million Australians heading into retirement over the coming decade, plus a sharp new focus on high-risk lead generation and superannuation-switching misconduct.
Cyber’s promotion captures the decade in miniature. It appears in 2016 as one half of an abstract “digital disruption and cyber resilience” challenge, becomes a standalone strategic priority in 2021, and by 2026 is embedded across the plan. ASIC even commits to its own “multi-year cyber resilience program,” acknowledging that the regulator itself is a target.
The framing of business has also shifted. The 2016 and 2021 plans largely treat industry as a population to be surveilled and, where necessary, disciplined. The 2026 plan, without abandoning that stance, adds an explicit productivity-and-growth mandate handed down in a new Statement of Expectations, reflecting a broader political shift toward reducing regulatory burden. That tension, between protecting consumers and unlocking investment, is now stated openly as the central balance ASIC must strike.
And the regulator is simply bigger. ASIC’s total budgeted resources for 2026–27 sit near $688 million, up 7% year on year, with most costs recovered from industry under the industry funding model, a mechanism that barely featured in the 2016 framing. It is better funded and more explicitly resourced against named priorities than it was a decade ago.
What it means for regulated businesses
Read together, the three plans trace an arc. A regulator that in 2016 was still building the capability to understand, that by 2021 had been pushed to enforce, and that by 2026 is enforcing with confidence while being asked to enable growth.
For anyone operating in financial services, markets or consumer credit, the practical takeaways from the 2026 plan are clear. ASIC’s gaze has moved decisively toward private markets, private credit and alternative investments, toward the safe adoption of AI, toward operational and cyber resilience as systemic issues, and toward the protection of superannuation and retirement savings. It arrives at those targets as a regulator that no longer needs to prove it will litigate, because it already has.
The corporate plan has always been a signalling document. Ten years on, the signal is being sent by a more confident, better-resourced and more sharply targeted regulator than the one that wrote the 2016 edition in the aftermath of the financial crisis. Businesses that treat the plan as advance notice, rather than an annual formality, will be the ones best placed for the four years ahead.

PX Partners helps organisations interpret and respond to the regulatory environment. This article is general commentary based on ASIC’s published corporate plans and is not legal or compliance advice.
Categories
Uncategorized

Don’t let perfection be the enemy of Reasonable Steps!

Almost five years on from the commencement of the Design and Distribution Obligations (DDO) in October 2021, the expectations around how Fund Issuers oversee their distributors have moved on considerably. ASIC’s work – including Report 795 on compliance with the reasonable steps obligation – has made clear that oversight of distribution is not a box-ticking exercise completed once and filed away. It is an ongoing, holistic discipline.

And yet, in trying to get it perfect, some Issuers risk doing very little. The reasonable steps obligation in s994E of the Corporations Act does not demand a flawless, exhaustive audit of every distributor. It demands reasonable steps – proportionate to the product, the target market and the degree of harm that could result if distribution goes wrong. The trap is treating due diligence as an all-or-nothing project. Waiting until you can build the perfect programme too often means the real, practical steps that would actually improve outcomes never get taken.
So what does “good” look like today? Across the Issuers who are aligning well to regulatory expectations, four themes stand out.

1. Connecting the dots across your distribution data
Distribution oversight has too often been run in silos: complaints sit with one team, significant dealing reports with another, and distributor due diligence somewhere else again. Issuers who are getting this right are joining those data points together. A cluster of complaints about a particular distributor, an unexpected significant dealing notification, and a due diligence response that glosses over sales practices are far more meaningful read together than in isolation. Reasonable steps are best understood as a holistic assessment of an entity’s full framework of controls – not a series of disconnected activities – and that same logic applies to the data an Issuer already holds.

2. A dynamic and responsive approach – not just the annual cycle
An annual due diligence questionnaire remains a sensible backbone, but it should not be the whole story. ASIC’s observations point squarely at the limitations of a static, once-a-year snapshot: circumstances change, regulatory action and corporate activity create an additional layer. Leading Issuers supplement the annual cycle with responsive, event-driven review – asking follow-up questions when a response is generic or incomplete, revisiting a distributor when complaints or dealing data suggest something has shifted, and refreshing their view when a product or its TMD is updated. This is precisely the kind of iterative, follow-up behaviour ASIC highlighted as better practice in Report 795.

3. A risk-based approach, viewed through a customer lens
Reasonable steps are, by definition, proportionate. That means devoting the most effort to the areas of highest risk – higher-risk products, narrower target markets, less mature channels – rather than spreading a thin, uniform layer of scrutiny across everyone. The most effective Issuers calibrate their attention to where the potential for consumer harm is greatest, and they frame the question through a customer lens: how does the distributor align practices with expectation of the Fund Issuer in seeking to limit distribution to the target market.

4. Leveraging systems and data for efficiency – for both sides
Finally, the Issuers making real progress are using technology to make oversight efficient for everyone involved. Chasing responses by email, version-controlling Word documents and hunting through drives and inboxes for missing answers is not just painful – it actively works against good oversight, because effort is consumed by administration rather than analysis. A well-designed system reduces the burden on distributors (who answer once) and on Issuers (who review in one place), freeing both to focus on what actually matters: understanding the distribution and evidencing the reasonable steps taken.

Where Know Your Distributor (KYD) fits
This is exactly the problem Know Your Distributor (KYD) was built to solve. KYD is a complete solution that takes the pain out of distributor due diligence for Australian Fund Issuers and Distributors. It gives product issuers a secure, efficient and meaningful way to monitor the distributors of their fund products – and, critically, to evidence the reasonable steps expected under their Design and Distribution Obligations.
KYD is owned and supported by PX Partners, whose practitioners bring real-world experience of the DDO. The solution is powered by Carne Group technology – a platform that exists and is in use today, deployed in over 75 countries, used to monitor more than 2,000 distributors globally, and relied upon by clients who collectively manage over $1 trillion in assets. It is ISO 27001 certified, hosted on AWS with leading cyber-security. The KYD DDQ is the Australian questionnaire is designed by Australian practitioners with input from a range of Australian Fund Issuers and Distributors.

A questionnaire built for deeper review – beyond the FSC baseline
The KYD due diligence questionnaire is aligned to the Financial Services Council (FSC) standard DDQ, so it covers the industry baseline Issuers already recognise. On top of that, it includes additional KYD-developed sections that allow for a broader and deeper review, with consistent, closed-form questions that make answering easier while capturing more detail for meaningful analysis. Coverage spans:
• company information and ownership
• regulatory status
• product governance arrangements
• distribution and sales practices
• governance, risk, compliance and assurance
• training
• business continuity, and
• a dedicated financial crime section – which has taken on heightened importance following the significant changes to Australia’s AML/CTF regime that commenced on 31 March 2026, moving compliance toward a more risk-based, outcome-focused model.
In other words, KYD gives Issuers a richer, more structured evidence base than the industry-standard DDQ alone – the kind of information that lets you connect the dots described above, rather than simply file another completed form.

How it works
KYD centres on a dynamic, industry-aligned questionnaire built specifically for the Australian market, and runs the whole process end to end through one system. The KYD team arranges for your distributors to complete the in-system questionnaire; distributors answer once and control which product Issuers can view their responses. Issuers then review those responses in a single central record – seeking clarification, uploading supporting information, recording assessments and tracking completion in one place. KYD performs the follow-up of questionnaire responses, leaving you free to focus on the commercial relationship and your own assessment.
The efficiency dividend is substantial: based on analysis undertaken by clients of the underlying Carne technology, the KYD solution could save over 80% in person-days compared to running the same activity manually.

Independent review service by PX Partners
For Issuers seeking greater assurance, KYD offers an optional independent review delivered by the risk and compliance specialists at PX Partners, who have extensive experience with the DDO and broader regulatory compliance. The review pre-vets distributor responses before they reach you, enabling your teams to focus on the highest-risk areas. As part of that service, PX Partners:
• verifies corporate and licensing information against ASIC records, AFSL authorisations and appointed auditors;
• reviews complaints handling by assessing website information and confirming AFCA membership;
• performs financial crime screening, including PEP, sanctions and adverse media checks on the distributor and its directors; and
• benchmarks each distributor against peers to provide comparative insights.
The output is a board-ready report containing DDQ assessment results, RAG-rated findings, executive summaries, key exceptions and practical commentary – exactly what governance forums need to make informed oversight decisions, and to evidence that reasonable steps were taken.

The bottom line
The reasonable steps obligation was never about achieving a theoretical ideal. It was about putting adequate systems, policies and practices in place to address the risks of distribution going astray – and being able to show it. Issuers who connect their data, stay responsive between annual cycles, focus effort where consumer risk is greatest, and lean on systems to do the heavy lifting are meeting that expectation today.
Don’t let perfection be the enemy of reasonable steps. Take the practical ones – and let KYD make them efficient.
To find out how KYD can support your distributor oversight, visit knowyourdistributor.com.au or contact the team at PX Partners.

Categories
Uncategorized

AI in Governance, Risk & Compliance: Regulators begin the call to action

Artificial Intelligence (AI) has rapidly evolved from experimental use cases such as document summarisation and basic automation to being embedded across critical processes within Australian financial services via agents and automation of key activities and tasks. On the cybersecurity front, frontier AI models have accelerated the risk of external threat vectors with actors now better equipped to target organisations. In April 2026, APRA issued an open letter to regulated entities following targeted engagement with banks, insurers, and superannuation trustees. The findings across entities were consistent and illustrated that AI adoption was progressing at pace while change management controls, information security and governance frameworks were struggling to keep up.

At a Board level, APRA observed strong interest in AI’s strategic and commercial potential, particularly in driving productivity, efficiency, and customer experience. However, Boards were not consistently able to demonstrate the technical literacy required to effectively challenge and oversee AI-related risks. APRA specifically noted an overreliance on vendor presentations and high-level summaries, without sufficient independent scrutiny of underlying risks of AI adoption and the specific impacts to customers and organisations.

In May 2026, ASIC reinforced this message through its own open letter to Australian Financial Services (AFS) licensees, calling for urgent uplift in cyber resilience. ASIC highlighted that frontier AI models are significantly accelerating the capability and accessibility of sophisticated cyber-attacks, allowing vulnerabilities to be identified and exploited at unprecedented speed and scale. ASIC’s message to industry was unambiguous: entities should not wait for further sophisticated AI developments before addressing their cyber resilience fundamentals and should act now with urgency, focus and accountability. Though an external lens to consider, it highlights that AI adoption is here now and the rapid pace of change and adoption represents significant risks to not only organisations but ultimately the end customers.

Both APRA and ASIC have shifted scrutiny towards Boards and senior executives, reinforcing that AI governance is not solely a technology responsibility, but a broader governance and risk management issue. This regulatory posture puts risk management back at the heart of AI adoption – CROs now need to consider what risk this change poses and how to manage it.

AI Adoption and Acceleration of Threat Vectors

This regulatory focus is underpinned by two related dynamics: the risk organisations and their service providers take on through adoption of AI and the acceleration of threat vectors that AI now enables.

One area of challenge facing organisations is that AI adoption risk is no longer confined to formally approved AI transformation programs or initiatives. Increasingly, AI capabilities are being embedded into everyday business tools, SaaS platforms and third-party solutions, often without the explicit label of “AI”. Each point of adoption can shift an organisations risk tolerances and resilience settings. The question for entities is whether this drift is being appropriately captured in governance and risk processes and factored into resilience assessments, rather than only becoming visible once something goes wrong.

At the same time, frontier AI is lowering the skill and cost required to identify and exploit vulnerabilities and is also creating new avenues for attack that traditional security controls were not designed to detect. A growing area of concern is the emergence of indirect prompt injection attacks, often referred to as “poison pill” or “thread needle” attacks where malicious instructions are hidden inside content that an AI agent later processes. An AI agent with legitimate access to enterprise systems can be manipulated through publicly accessible content that it is instructed to analyse, summarise or act upon. No traditional intrusion may occur, yet the outcome can still compromise data integrity, confidentiality or operational controls. As organisations increasingly deploy AI agents across business functions, the threat environment evolves and the scope of cyber security must expand with it. Understanding where AI agents are operating, what systems they can access and how they can be influenced by external content is rapidly becoming a core component of cyber resilience.

These impacts are compounded by service providers and third-party vendors, many of whom are embedding AI capabilities into their products and service. AI-related risks can be inherited through the supply chain with limited visibility over how these capabilities operate and are governed. Importantly AI-related risks rarely sit within a single risk category. Vulnerabilities can quickly cascade into broader risks such as privacy, conduct and operational resilience and reinforces AI as across-cutting risk theme as opposed to a standalone item on a risk register.

Integrating AI Into Existing Frameworks

Australia’s principles-based regulatory approach means that existing frameworks remain relevant and the focus for entities is on integrating AI into their existing governance structures and risk management frameworks. At the same time, organisations can also draw on global reference frameworks, such as the EU AI Act, ISO 42001, and the NIST AI Risk Management Framework to inform areas such as risk classification, monitoring, and assurance. This combined approach anchors governance in domestic regulatory requirements while leveraging international standards to fill capability and maturity gaps.

CPS230 Implications

For APRA-regulated entities and service providers across the value chain, CPS 230 (Operational Risk Management) provides a clear pathway for embedding AI governance. Although not explicitly AI-focused, it applies to all critical business processes and by extension, captures AI to the extent it is embedded into these processes.

  • Operational Risk Management: – Entities must identify and assess AI-specific risks prior to deployment, including model error, data bias, and disruption states that may not be immediately visible.
  • Critical Operations – AI systems supporting critical operations require enhanced governance, including defined disruption tolerances, recovery objectives, and tested fallback arrangements. Additionally, considerations on how AI impacts resiliency and service continuity
  • Material Service Providers – Most AI vendors will meet the materiality threshold under CPS 230, requiring formal agreements, ongoing monitoring, and clearly defined exit strategies.
  • Business Continuity – AI failure scenarios must be incorporated into business continuity plans and tested regularly.

Regulatory Expectations for Uplift

APRA’s open letter to industry clearly articulates regulator expectations and next steps for entities. ASIC’s subsequent communication reinforces and cross-references APRA’s position, signalling that these expectations apply broadly across regulated financial services organisations.

Taken together, the following represent the minimum expectations communicated by regulators:

  • Establish an AI governance framework – AI governance should be embedded into the enterprise-wide Risk Management Framework with policies, standards and accountability structures established, including clear ownership across the AI lifecycle. This includes maintaining a live inventory of AI tools and use cases with defined ownership across the full lifecycle.
  • Upgrade third-party and supplier risk management – Map the full AI supply chain including fourth-party dependencies and review AI vendor contracts to include appropriate controls such as audit rights, notification of model updates, incident reporting and exit provisions where necessary.
  • Concentration risk – SNOW and MSPs are increasingly reliant on a small pool of frontier AI models, warranting explicit third-party risk assessments in the same way concentration in cloud infrastructure providers is managed.
  • Update cyber resilience controls – Review and validate core security controls against AI-accelerated threat scenarios. This includes strengthening identity and access management for non-human actors, patching cadences, penetration testing and incident response plans. Cyber resilience controls must be demonstrably working and not just documented.
  • Implement integrated & continuous assurance – Entities should establish effective assurance mechanisms across cyber security, data governance, model performance risk, operational resilience, privacy, and conduct risks. Second line and internal audit functions must have sufficient capability and tooling to independently assess AI systems, with risk and security assessments conducted pre-deployment and on a continuous basis.
  • Ensure board-level oversight is substantive – Boards should receive clear, evidence-based reporting on AI and cyber risk, including control effectiveness, testing outcomes, and incidents, supported by defined escalation triggers. Oversight should enable informed challenge rather than high-level summaries of AI tools in use.
  • Uplift Board and Executive AI capabilities – Implement targeted training programs on AI risk, controls and regulatory expectations, ensuring Boards have sufficient AI literacy to effectively challenge and direct the business.

The Path Forward

Looking ahead, regulatory scrutiny is expected to increase. APRA has indicated further supervisory focus on AI-enhanced risk, while broader regulatory developments such as the Privacy Act reforms coming into effect December 2026 will introduce additional requirements relating to automated decision-making transparency.

Organisations that proactively embed AI within their governance, risk, and resilience frameworks will be better positioned to meet these expectations and demonstrate effective oversight in an increasingly complex risk environment.

Categories
Uncategorized

Investment governance under the microscope: Has risk and compliance kept pace with in-house investment management?

APRA has sharpened its expectations on investment governance and, over the past year, begun backing them with enforcement. The standards apply with equal force whether a Trustee outsources investment management, runs it in-house, or operates a hybrid. Our concern, drawn from years leading risk functions inside investment managers, is a quieter one that the enforcement headlines have yet to reach: as more funds have brought investment management in-house, has the risk and compliance capability meant to support it kept pace?

Over the past decade a growing number of superannuation funds have internalised investment management. The stock pickers, deal teams and portfolio management capability now sit inside the Trustee, and that investment capability is usually well built out. The second and third lines have often had less time and investment to scale alongside it. Independent oversight and challenge of the investment function is demanding work, and the risk and compliance capability to match a maturing in- house investment team takes time to build.

There is a good reason attention has sat elsewhere. In superannuation, the functions closest to the member naturally command the most focus. Complaints, death and disability claims, member disclosures, and the core business of accepting contributions and paying benefits are visible, time- critical and emotionally significant. It is understandable that risk and compliance effort has concentrated there. Investment governance, by contrast, can feel remote from the member, until a valuation dispute, a unit pricing error or a poorly monitored option makes it very close indeed.

This article sets out why the same rigour Trustees expect of their outsourced managers should be turned inward, and what recent regulatory activity tells us about the cost of leaving that gap open.

The standards converging on investment governance

Investment governance in superannuation rests first on SPS 530 Investment Governance, which has applied in its strengthened form since 1 January 2023. Under SPS 530 a Trustee must prudently select, manage and monitor investments, and maintain an investment governance framework appropriate to the size, business mix and complexity of its operations, with the board ultimately responsible. The strengthened standard sharpened expectations on valuation governance, liquidity management and stress testing, the same areas APRA and ASIC have found wanting in its review of unlisted asset valuations.

SPS 530 does not operate alone. SPS 515 Strategic Planning and Member Outcomes ties investment decisions back to the outcomes members receive. From 1 July 2025, CPS 230 Operational Risk Management added a resilience layer. It treats investment management as a critical operation or material service whether the function is outsourced, internalised, or a combination of both, and it raises the bar on how Trustees identify and oversee the service providers they depend on, including the fourth parties sitting behind their direct providers. Since early 2025, the Financial Accountability Regime has placed named, personal accountability on Trustees, their directors and senior executives. Accountability, in APRA’s words, cannot be outsourced.

Taken together, these requirements ask Trustees to govern the substance of investment decisions, connect them to member outcomes, make the function operationally resilient, and stand behind it personally. The distinction APRA is now testing is not whether a function was competently procured, but whether it is competently governed on an ongoing basis. That answer must hold wherever the function sits, and for many Trustees it is easier to give for what they outsourced than for what they built themselves.

The gap that has opened up in-house

A common assumption is that internalisation reduces governance risk, because the Trustee now controls the function directly. We are curious at to whether that consistently holds true. An outsourced relationship sits inside a contracted framework: there are service levels, defined reporting, due diligence rights, and a counterparty that is itself regulated. When a fund brings investment management in-house, that external scaffolding falls away, and it is not always replaced with an equivalent internal control environment.

Internal investment teams typically grow out of a small initial footprint and scale quickly alongside funds under management. The second and third lines often do not grow at the same rate. Risk and compliance coverage of the investment function often lags the front office in both capability and resourcing. Many Trustees lack a dedicated second line with the technical depth to challenge portfolio managers on execution quality, counterparty selection, mandate adherence and the conflicts specific to managing money in-house. Valuation governance for unlisted assets is particularly sensitive, since the investment team whose performance is judged on those assets often has the deepest knowledge of them and, without clear separation, can end up influencing how they are valued.

It is worth asking whether the internalisation of investment management was matched by a corresponding uplift in the risk and control functions that oversee it, and whether the same standard of due diligence, monitoring, control assurance and conflicts management a Trustee expects of an external manager would hold if applied to the internal team. For many funds, that is still developing. The opportunity is to bring the internal control environment up to the standard already expected of outsourced investment management.

Having led risk and compliance functions inside investment managers, the PX Partners team has seen this from the inside. We know how quickly an internal capability can outgrow the controls around it, and how easily independent oversight becomes an afterthought when the investment team is delivering.
The point is not that in-house management is wrong. It is that it carries obligations Trustees cannot meet by governing the internal team more lightly than they would an external one.

One lens, wherever the function sits

CPS 230 and SPS 530 apply the same test regardless of the operating model. CPS 230 asks the operational questions: can you identify the critical operation, understand its dependencies and the
providers behind it, set tolerances for disruption, monitor against them, and respond when something fails? SPS 530 asks the substantive ones: can you evidence that investments were prudently selected and are being properly monitored and valued? Neither standard cares whether the function is run by a third party or by a team down the corridor. The Trustee owes the same answer either way.

Where Trustees run more than one model, there is an additional layer to manage. Hybrid arrangements, with some asset classes managed internally and others left with external managers, create a coordination point between the two that benefits from clear ownership. It is worth checking that the standard applied to external managers also informs the internal approach, and that member facing impacts have a clear owner rather than sitting between functions.

Where the gaps typically appear

  • For outsourced functions, the recurring weakness is what happens after onboarding. Initial due diligence tends to be thorough. Ongoing oversight then narrows to performance reporting, an annual due diligence questionnaire and the occasional site visit. Operational risk indicators, control attestations, visibility into sub-custodians and sub-advisers, business continuity testing and exit planning are often underdone. CPS 230 has raised the bar here, extending the
    expected depth of oversight beyond the direct provider to the fourth parties they in turn rely on.
  • For internalised functions, the gaps are structural. A common gap is second-line depth: the specialist skills needed to challenge the front office on investment risk take time and investment to build. Compliance coverage of trade execution, mandate adherence and conflicts of interest is often still maturing. Valuation governance for unlisted assets warrants particular attention.
  • For hybrid models, the risks of both combine.

What APRA has signalled

APRA has put its focus on investment governance beyond doubt. On 7 October 2025 it wrote to platform Trustees, following a thematic review covering Trustees responsible for around 95 per cent of platform assets, calling for stronger action on investment governance (the accompanying letter is available here). Two of its findings travel well beyond platforms. First, a Trustee’s core duties are the same irrespective of its business model. Second, accountability for deciding what belongs on the menu, and for the outcomes members experience, stays with the Trustee no matter how many parties sit in between.

APRA has since acted on those findings. On 17 December 2025 it accepted a court-enforceable undertaking from Netwealth Superannuation Services over the depth of due diligence and monitoring applied to onboarded options and the management of related-party conflicts, and imposed additional licence conditions on Equity Trustees Superannuation the following day. It has since taken action against further platform Trustees, including HTFS Nominees, the Trustee of the HUB24 Super Fund, in May 2026. The detail cuts against a comfortable assumption, that outsourcing investment management reduces the governance burden. It does not. The same logic runs in the other direction: bringing the function in-house does not reduce it either. APRA&’s Deputy Chair has said the platform segment will remain a supervisory priority throughout 2026, and the events sitting behind these actions, including the First Guardian and Shield collapses, have produced member losses and compensation running into the hundreds of millions. The stakes of weak investment governance are no longer hypothetical.

What separates mature Trustees

Across our engagements with Trustees running internalised, outsourced and hybrid models, three themes consistently separate mature investment governance from the rest.

1. Govern the function, not the form. Internal investment teams should be held to the same standard as external managers: documented mandates through investment policies, performance and risk monitoring, control assurance, conflicts management and contingency planning. The test is simple. If you would expect an external manager to produce it, your internal team should produce it too.
2. Build the second and third line to match the first. Investment risk and compliance need real technical depth. Investment risk management keeps strategies running true to label, but the area that most often needs attention is the expertise to review and challenge front office controls, such as execution quality and counterparty selection, and to understand the conflicts unique to managing money in-house. For Trustees with internalised capability, this is often where the greatest investment is required.
3. Anchor everything in member impact. Investment governance is not a back-office discipline. Unit pricing errors, delayed switches, valuation disputes and performance issues flow downstream from investment management to the very member-facing activities that already command a Trustee’s attention. Tolerances under CPS 230, and objectives under SPS 530, should be set against member outcomes, not internal service levels alone.

Why Trustees should act now

APRA’s focus has shifted from documentation to demonstration, and the events of late 2025 show what that shift looks like in practice. The question is no longer whether the material service provider register is current. It is whether the tolerances, controls and oversight hold when tested, and whether the Trustee can show it, for the functions it runs as much as the ones it buys.

This cannot be retrofitted on a supervisory timetable. Building second and third line technical depth takes time. Setting tolerances and objectives that connect to member outcomes, and testing them under stress, takes longer still. Trustees who start now will have something defensible by the time it is tested. Those who wait will be assessed against what their peers have already done.

In our experience, the Trustees getting ahead of this are interrogating their in-house investment governance against SPS 530 and CPS 230, testing whether they can evidence the same rigour internally as they expect of their external managers. Having sat on both sides of that question, inside investment managers and now advising Trustees, we think it is the right one to be asking.

Categories
ausbiz 

The wake-up call for Superannuation Trustees: Bridging the financial crime gap

The regulatory imperative

ASIC’s recent directive to superannuation trustees represents more than regulatory oversight – it signals a fundamental shift in expectations for an industry custodian of $4.3 trillion in Australian retirement savings. While the regulator’s February 2026 review focused on scam prevention, it exposed a broader truth: superannuation trustees must urgently strengthen their entire financial crime framework with members losing $22 million to super-related scams in 2025 alone.

ASIC Commissioner Simone Constant’s warning extends beyond scams: “As banks, telecommunications providers and other financial service businesses increase their anti-scam and anti- fraud capabilities, superannuation trustees must do the same or risk becoming a soft target.”

At PX Partners, our work across financial crime risk management reveals that successful prevention requires understanding the interconnected ecosystem of predicate crimes, money laundering, fraud, scams, and downstream threats like terrorism financing.

Understanding the financial crime ecosystem

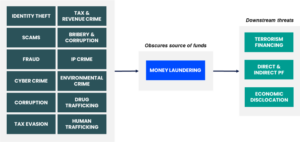
Financial crime is not a series of isolated threats but an interconnected system where each element fuels and enables the others. Money laundering sits at the centre, serving as the mechanism that allows criminals to enjoy proceeds from predicate crimes – ranging from fraud and cybercrime to corruption and human trafficking.


Fraud – Scam – ML relationship

It is important to understand the concepts at play and the interrelationship between them:

  • Fraud is deception for personal gain or to cause loss to another. As a predicate crime, it generates proceeds requiring laundering;
  • Scams are a fraud subset and involve manipulating victims through social engineering (often using digital channels) to fraudulently transfer funds. A familiar example is pig-butchering which combines romance fraud, investment scams, cybercrime, and often human trafficking, with proceeds laundered through cryptocurrency; and
  • Money laundering is the process of obscuring the criminal origin of proceeds through placement, layering, and integration into the legitimate financial system.

What ASIC found?

ASIC’s recent review of 47 superannuation trustees focussed on the availability, quality and actionability of anti-scams and fraud content, including by checking the website content for clarity and relevance, prominence on the website and readability. The review found that banks scored positively in over 80% of criteria assessed, whereas most super funds scored positively against just 40–60% of the same criteria. This was a narrow review focussed on public facing content but may be viewed by the Regulator as an indicator of broader weaknesses in the financial crime framework.

Previous ASIC reviews have called out other gaps in the financial services industry that has immediate relevance for Superannuation Trustees:

1. Strategic Gaps: No organisation-wide scams OR fraud strategy. Inadequate integration with broader financial crime frameworks.

2. Operational Weaknesses: Over-reliance on identity verification while missing manipulation indicators. Limited transaction monitoring for scam typologies. No distinction between unauthorised fraud (identity theft) vs authorised fraud (scams where members are manipulated) where different approaches are required to manage the risk.

3. Governance Blind Spots: Insufficient oversight of administrators’ controls. Weak connection between cyber incidents and financial crime response. Limited board reporting on financial crime holistically.

An integrated financial crime framework

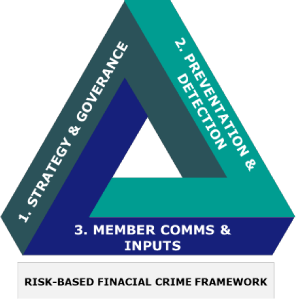
Drawing from ASIC’s REP 761 & 790, APRA’s SPG 223, AUSTRAC guidance, and our implementationexperience, we recommend an integrated three-pillars approach to managing this risk:

Third-Party Risk:Map third-party controls across the spectrum: transaction monitoring, cyber defences, fraud analytics, and scam detection. Ensure visibility into administrator capabilities and regular testing.

Pillar 2: Prevention and detection

Cyber as Predicate: Recognise cyber incidents as predicates to fraud / scams. Implement enhanced monitoring post-breach. Link IT security with financial crime teams.

Integrated Detection: Deploy scam-specific rules identifying manipulation (urgency, inconsistent requests, new beneficiaries). Complement traditional fraud detection (unauthorised access) with authorised fraud indicators.

Friction Points: Cooling-off periods for high-risk transactions. Multi-channel verification. Real-time alerts on unusual patterns. Enhanced due diligence for sudden behavioural changes.

Pillar 3: Member communications and victim support

Transformed Communications: Prominent scam/fraud warnings. Clear examples of common typologies (early release scams, pig-butchering, invoice fraud). Dedicated reporting channels (only 20% of funds provide this). Demographic-specific education.

Victim Support: Streamlined reporting processes. Trauma-informed victim support. Clear escalation paths. Integration with AFCA and law enforcement.

Where do I start?

If you are starting from a low level of maturity, it is important to do a risk-based prioritisation – you can’t do it all at once! Where you’ve already established a financial crime operating model, it’ll be targeted uplift to meet the upcoming reforms by 31 March 2026.

0-3 months Conduct gap analysis across full financial crime spectrum. Review website content for scams and fraud. Establish reporting channels. Appoint senior owner.
3-6 months Document integrated financial crime strategy. Map administrator controls. Implement transaction friction. Deploy awareness campaign.
6-12 months Develop detection rules spanning fraud, scams, and ML typologies. Enhance training on financial crime ecosystem. Establish integrated board reporting.

Ensure that existing frameworks are leveraged as much as possible. We see successful entities:

  • designating financial crime (not just scams) as FAR key responsibility.
  • mapping scam/fraud risks into CPS 230 operational risk assessments.
  • integrate with AML/CTF programs as scams and fraud are predicate crimes for money laundering.

The path forward

Scams don’t exist in isolation – they’re part of a continuum spanning predicate crimes, money laundering, and downstream threats.

ASIC’s scam focus is the catalyst, but the solution must be comprehensive. Trustees who understand the fraud – scam – ML relationship and implement an integrated approach will not only meet regulatory expectations but genuinely protect members from an evolving threat landscape.

At PX Partners, we’ve supported financial services organisations in developing holistic financial crime solutions that connect AML/CTF, fraud prevention, scam detection, and cyber resilience. Our experience implementing integrated frameworks positions us to help trustees navigate this complex challenge and transform member protection from compliance obligation to competitive advantage.

The time to act is now. Trustees who embrace this integrated approach demonstrate a true desire to protect the wellbeing of their members in their role as fiduciaries and further strengthen protections against financial crime.

Categories
ausbiz 

What we’ve learnt in 5 years

Five years ago, we established PX Partners with a clear mission: to provide an alternative to the traditional consulting model by delivering practitioner led, client aligned, practical and sustainable solutions.

What began as a boutique consultancy has since grown into a trusted partner for a diverse portfolio of clients across the financial services landscape and beyond – particularly in funds management, superannuation, and insurance. Because we put our clients and their end-customers at the centre of our work, we’re proud to report that over 90% of our engagements come from our existing clients and referrals by our clients.

Along the way, we’ve navigated a global pandemic, regulatory upheavals and generational changes in technology. While the world around us has changed, our commitment has remained constant.

As we celebrate this milestone, we’re sharing five things we’ve learnt from our first 5 years supporting clients.

You can’t do more with less

One of the classic refrains in corporate life when costs are being cut. The need to do more with less. Which is a complete furphy. You can only do less with less. And that’s okay, as long as it’s transparent.

Cutting budgets for Risk and Compliance teams at a time when the regulatory burden is increasing is a fast track to bad outcomes. If you think compliance is expensive, try non-compliance!

Risk leaders need to be clear that having less means doing less – fewer controls monitored, slower incident response and less proactive risk identification. This isn’t about lowering standards. It’s about recalibrating expectations and being clear about what can realistically be achieved with the resources available.

This is not to say that you can’t find ways to make your processes more efficient and embrace new technologies. We have and continue to iterate and improve how we operate to deliver benefits to our clients and Risk & Compliance teams have a really important role to play here – not just in supporting or challenging business teams with risk-in-change and vendor oversight but also in surfacing solutions that can make risk and compliance processes more efficient.

At PX Partners, we’re lucky to be doing more with more having grown our team from our founding two to a team of twelve today across both Sydney and Melbourne.

Don’t fear the tough decisions

Governance around decision making is a key enabler of business success. We have seen so many examples (usually through court action by Regulators) of firms deferring and delaying making critical business decisions.

Whether it is a decision where to invest resource and effort or to make a difficult decision to exit a product or business line, those who are successful have the structures and governance in place to:

  1. Gather the right information
  2. Get it to the right people
  3. Do it in a timely fashion
  4. Commit and execute
  5. Learn from the experience.

Don’t let decision making be paralysed by Committees – good governance around decision making means empowered and accountable executives and not deference to Committee structures. Committees have an important role to play but should be used sparingly and not as a default.

In our own business, ensuring we align to our values helps guide our decisions and makes them easier. Our decisions are centred on being fair to ourselves and our clients, making things better, and being real and transparent about the reasons. That doesn’t mean decisions are easy, but anchoring to these values has resulted in fast alignment around difficult decisions.

People over technology every time

Now more than ever before, firms are looking to technology to deliver efficiencies and reduce cost. The advent of Generative Artificial Intelligence has only super charged this shift. The Fear of Missing Out (FOMO) is rife – firms are rushing to do something in the fear of being left behind. Technology is an enabler, not a silver bullet. Because at the end of the day, technology should serve people and strategy and not the other way around.

Take this thought experiment. How would you feel if we offered you a robot to do a bunch of your usual tasks well? Brilliant, we assume, as you could spend time doing more satisfying things. What if we instead offered your boss a robot to do your job well? Threatened or insecure perhaps? At PX Partners, we have been in the fortunate position to start with a blank slate unencumbered by legacy technology and systems. We want technology to serve our team and clients and therefore encourage our team to automate and streamline what they can and do it transparently and with accountability.

We have embraced technology to enable our team in supporting clients. Our Know Your Distributor (KYD) solution is a prime example: designed in collaboration with product issuers and distributors, KYD helps streamline due diligence for the whole industry.

No set and forget

In financial services, there’s often a trigger for refreshing risk frameworks, and most recently, APRA’s CPS 230 has prompted firms to take a hard look at their operational resilience and third-party risk settings. But this shouldn’t be a one-off exercise. Risk management is a verb not a framework.

This takes effort from the Boardroom to the front line. And deliberate focus. The tone from the top matters and sets the standard for the firm.

What does good risk management look like? Don’t overthink it – just start with something. Start measuring things – are they useful? If not, change it. Do you need a forum to discuss key risks? Set it up. If it’s not working, change it. It’s a verb. Just do it. Set a process and repeat it, improve it and reap the benefits.

At PX Partners, our risk mindset is essential to how we run our business. We take risks. We learn and respond. As a business servicing regulated clients, we have a high bar to meet. In truth, these are no higher than standards we set for ourselves – to keep improving. It underpins how we serve clients, manage our own business and partnerships, and make decisions. By treating risk as a continuous practice, we stay agile, accountable, and aligned with our mission to deliver trusted outcomes in a complex and evolving world.

Compliance does not conflict with customer outcomes

Doing the right thing always wins in the end. It might not always seem that way but it is true.

We see compliance not as a constraint, but as a catalyst for better customer outcomes. In financial services, it can often feel that compliance with regulatory requirements is just that – a tick the box exercise. But it is not just about meeting the regulatory requirements, it’s about building trust, transparency, and resilience. When compliance is embedded thoughtfully into processes, it strengthens the quality and reliability of the products & services. Regulatory enforcement is littered with examples of firms who should have invested early in robust compliance and governance – from fees for no service to recent MIS failures. A commitment to meaningful compliance from all firms in the chain could have avoided these adverse outcomes for clients.

At PX Partners, we are hugely proud of the level of repeat client work. We don’t shy away from telling our clients what we think is right for them and their end customers. These clients are working with our team to invest in governance, risk and compliance to uplift and enhance what they do which ultimately benefits end customers.

Categories
ausbiz 

Investment Management CPS 230 Webinar

PX Partners recently hosted a webinar exploring what it means to be a CPS230 “Material Service Provider” (MSP) in today’s regulatory and operational landscape. The session covered practical insights and key considerations across the following areas:
  • Roles and responsibilities as an MSP
  • Taking a practical approach to process mapping
  • Establishing effective risk management settings
  • Aligning Business Continuity Plans (BCPs) and Disaster Recovery (DR) strategies
  • Meeting enhanced Due Diligence requirements

Categories
ausbiz 

Risk & Reform Webinar – Insights on AML/CTF, CPS230 and ASIC Compliance Plans

PX Partners recently hosted a webinar to share practitioner insights on:

  • AML/CTF Changes –
    what to watch ahead of AUSTRAC’s 2026 AML/CTF reforms
  • CPS 230 –
    enhanced expectations of APRA-regulated entities and downstream impacts on Material Service Providers (MSPs)
  • Compliance Plans and Controls Uplift –
    aligning with evolving APRA and ASIC expectations

Categories
ausbiz 

Rethinking Scheme Compliance Plans: A Risk-Based Imperative for Responsible Entities

In light of the Australian Securities and Investments Commission’s (ASIC) recent review into  compliance plans across the managed investment industry, Responsible Entities (REs) are being urged to move beyond a legalistic, checkbox approach and adopt a more robust, risk-based mindset. The findings, published in ASIC’s media release 25-090MR, reveal systemic deficiencies in Compliance Plans and large scale non-compliance with Regulatory requirements. 

The Compliance Plan Wake-Up Call

ASIC’s review of 50 compliance plans – covering 1,471 funds and nearly $1 trillion in assets – found that most failed to adequately address key Regulatory obligations. These include:

  • Design and Distribution Obligations (DDO) under Part 7.8A of the Corporations Act;
  • Internal Dispute Resolution (IDR) systems under s912A(1)(h) and associated regulations; and
  • Reportable Situations (RS) under Subdivision B, Division 3 of Part 7.6.

Alarmingly, some compliance plans did not address DDO at all, suggesting they had not been meaningfully reviewed since the regime’s introduction in 2021. ASIC Commissioner Alan Kirkland noted, “Failing to plan is planning to fail,” underscoring the critical role compliance plans play in safeguarding retail investors.

From Legal Formalism to Risk Management

Historically, many Responsible Entities have relied heavily on their legal advisers to draft compliance plans. While lawyers play a vital role in identifying and interpreting the relevant legislative obligations, this approach often results in documents that are technically compliant but operationally ineffective.

What’s missing is the practical application of those obligations – how they are controlled, monitored, and assured in day-to-day operations. This is where risk managers must step in. Risk professionals are best placed to:

  • Translate legal obligations into operational controls;
  • Design assurance mechanisms that test the effectiveness of those controls;
  • Identify gaps and emerging risks; and
  • Ensure the compliance plan evolves with the business and Regulatory landscape.

This shift aligns with ASIC’s broader Regulatory expectations, particularly those outlined in Regulatory Guide 259 (RG 259), which emphasises the need for Responsible Entities to maintain adequate risk management systems under s912A(1)(h) of the Corporations Act. RG 259 complements RG 132 by reinforcing that compliance is not just about documenting obligations – it’s about embedding risk awareness and control effectiveness into the operational fabric of the organisation.

Tailoring Compliance to Scheme-Specific Risks

A key theme emerging from ASIC’s review is the need for compliance plans to reflect the specific risks of each registered scheme. Too often, REs rely on generic templates that fail to consider the unique features, investment strategies, and operational risks of individual schemes. This undermines the effectiveness of the compliance framework and exposes investors to risk.

To meet ASIC’s expectations, REs must be able to demonstrate that their compliance plans:

  • Identify the particular risks associated with each scheme;
  • Include controls that are tailored to those risks;
  • Provide for regular testing and review of those controls; and
  • Are updated in response to changes in the scheme’s structure, strategy, or Regulatory environment.

This was reinforced in ASIC’s recent correspondence with Responsible Entities, where the Regulator raised concerns that some compliance plans did not adequately identify relevant obligations or appropriate controls, and that the same plan was being used across multiple schemes without sufficient customisation.

ASIC’s Direct Engagement with REs

In a clear signal of its intent to drive reform, ASIC has begun writing directly to Responsible Entities whose compliance plans were found wanting. These letters have urged REs to review and modify their compliance plans in line with RG 132 and the findings of the review. ASIC has also reminded REs of their obligation to lodge modified plans under s601HE(3) and to consider their breach reporting duties under the Corporations Act.

What This Means for Responsible Entities

The message is clear: REs must treat compliance plans as living documents that reflect a genuine understanding of their Regulatory obligations and the risks inherent in their operations. This means:

  • Moving beyond generic templates;
  • Embedding compliance into operational processes;
  • Ensuring board and senior management oversight;
  • Tailoring controls to scheme-specific risks; and
  • Being proactive in identifying and addressing gaps.

ASIC has signalled that it will continue to monitor compliance plans and may take enforcement action where deficiencies persist.

What to do?

For Responsible Entities, the time to act is now. Drafting, reviewing and approving takes time. ASIC is expecting industry to act quickly given the issues highlighted in their review. 

PX Partners works with REs to draft fit for purpose and pragmatic Compliance Plans which align with Regulatory requirements and expectations. 

Jon O’Keeffe is the author of this article. Jon provides regulated entities with pragmatic advice on governance anchored in more than 20 years of practitioner experience.

Categories
ausbiz 

Governance: The golden thread holding it all together

Depending who you ask, definitions of Governance vary wildly. Some see governance as something that Boards do, others as reporting or even as an administrative function that adds no value. To us at PX Partners, governance is at the heart of the organisation. It as is the linchpin that connects strategy with planning with risk management, obligations, reporting, and accountability. It is the mechanism through which organisations demonstrate their integrity, resilience, and compliance – especially under the weight of new regulatory expectations like APRA’s CPS 230 and the Financial Accountability Regime (FAR).

The Australian Institute of Company Directors (AICD) defines governance as “the systems that direct and control – or govern – an organisation.” It is fundamentally about relationships between the board, management, and stakeholders and the mechanisms by which authority is exercised and accountability is enforced. As the Hon. Justice Neville Owen described during the HIH Royal Commission, governance is “the framework of rules, relationships, systems and processes within and by which authority is exercised and controlled in corporations”.

This framing is particularly relevant in the current regulatory environment, where governance is not just a structural concept but a dynamic enabler of compliance, performance, and trust. Whether through formal board oversight or embedded operational controls, governance is the thread that weaves together the obligations and expectations placed on financial services entities.

Licensing Obligations: The Foundation of Governance

At its core, governance ensures that entities meet their general licensing obligations under the Corporations Act and ASIC’s Regulatory Guides. These obligations require financial services providers to:

  • • Maintain adequate risk and compliance frameworks.
  • • Deliver services efficiently, honestly, and fairly.
  • • Manage conflicts of interest and ensure appropriate oversight of representatives.

Governance is the structure that ensures these obligations are not only met but embedded in day-to-day operations. It defines who is responsible, how oversight is exercised, and how breaches are identified and addressed. As noted in governance also plays a critical role in how entities assess and report on their service providers, particularly in the context of due diligence and ongoing monitoring.

CPS 230: Governance in Operational Resilience

CPS 230 elevates governance from a compliance function to a strategic imperative. It requires regulated entities to:

  • • Map critical operations and define tolerances for disruption.
  • • Establish governance frameworks that ensure Board and Executive oversight of operational resilience.
  • • Formalise service provider arrangements with clear performance metrics, audit rights, and remediation protocols.

Governance under CPS 230 is not just about structure—it’s about action. Boards must receive regular reporting on risk exposure, service performance, and compliance. Executives must ensure that SLAs, risk assessments, and control testing are not only in place but actively monitored.

FAR: Personal Accountability in Focus

The Financial Accountability Regime (FAR) introduces a new layer of governance by making accountability personal. It requires entities to:

  • • Identify Accountable Persons and assign clear responsibilities.
  • • Maintain accountability maps and statements.
  • • Ensure that governance frameworks support the oversight of these responsibilities.

This means that governance is no longer just about committees and policies—it’s about traceability. As seen in State Super CPS 230 Support – PX Partners – v1.0 – 310125, aligning reporting lines from General Managers to Board Committees is now a regulatory expectation, not a best practice.

APRA’s Governance Review: Raising the Bar

In March 2025, APRA released a discussion paper  proposing eight key reforms to its core governance standards (CPS 510, SPS 510, CPS 520, SPS 520, and SPS 521). The review reflects APRA’s view that while governance practices have improved, significant weaknesses remain—particularly in areas such as director capability, board performance assessment, and conflict management.

The proposals aim to:

  • • Strengthen expectations around board skills, tenure, and independence.
  • • Introduce more prescriptive requirements for fitness and propriety assessments.
  • • Improve transparency and rigour in board performance evaluations.
  • • Clarify and tighten rules around conflicts of interest.

APRA’s message is clear: governance is not a “tick-the-box” exercise. It is a live, evolving discipline that must be embedded in the culture and operations of every prudentially regulated entity.

Governance as the Integrator

Governance connects the dots between:

  • • Risk Management: Ensuring that risk frameworks are embedded and aligned with Board and Executive oversight.
  • • Reporting and Oversight: Defining the cadence, content, and escalation pathways for risk and compliance reporting.
  • • Accountability: Mapping responsibilities under FAR and ensuring traceability of decisions and actions.

The Governance Imperative

In our work with clients across the financial services industry, we’ve seen that the most successful CPS 230 and FAR programs are those that treat governance not as a compliance obligation, but as a strategic enabler. Governance is what allows organisations to:

  • • Translate regulatory expectations into operational reality.
  • • Connect Board-level oversight with frontline execution.
  • • Demonstrate resilience, transparency, and accountability to regulators, customers, and stakeholders.

As the regulatory bar continues to rise, governance is no longer optional—it is the key that unlocks sustainable compliance and long-term trust.

Jon O’Keeffe is the author of this article. Jon provides regulated entities with pragmatic advice on governance anchored in more than 20 years of practitioner experience.